Partner with 227 InfoSec, to gain a dedicated security ally who will help you identify, mitigate, and prevent cyber risks!


A Service-Disabled Veteran-Owned Small Business with over 25 years of Department of Defense cybersecurity experience, 227 InfoSec delivers disciplined, mission-driven protection to commercial, tribal, and government organizations. Our team specializes in supporting the Defense Industrial Base (DIB) through comprehensive CMMC consulting, security program development, and risk-based assessments that align with NIST and DoD standards.
From CMMC preparation and assessment to vessel cybersecurity inspections and assessments aligned with the USCG Final Rule, 227 InfoSec delivers specialized cybersecurity expertise across regulated environments. Our services include expert-led facility/vessel assessment, including vulnerability identification and management; policy development; cybersecurity inspection and risk assessment; incident response planning; and manual and AI-driven penetration testing designed to identify risk, strengthen defenses, and maintain compliance.

We provide comprehensive CMMC consulting, mock assessments, and C3PAO 1099 assessor support. From initial gap analysis and policy development through control implementation, evidence validation, and assessment readiness, our certified professionals help organizations prepare for CMMC Level 2 while aligning with DFARS and NIST SP 800-171 requirements. We also support C3PAOs with experienced 1099 assessment professionals to augment assessment teams and meet engagement demands.

Our experts design and implement scalable cybersecurity programs built around your mission. We align governance, risk management, and incident response processes to industry frameworks like CMMC and NIST CSF, ensuring operational resilience and measurable security maturity.
227 InfoSec offers a comprehensive range of cybersecurity services to support your organization’s security journey. If you do not see exactly what you are looking for, contact us and our team will be happy to guide you in the right direction.
Our penetration testing services uncover weaknesses in your systems before attackers do. We provide two options to penetration testing (Automated AI, and Expert Manual). This gives our clients the best solutions to vulnerability discovery.
Not every security evaluation needs to be an all-out simulated attack. Our vulnerability assessments accurately identify vulnerabilities in your enterprise, helping you understand your weaknesses. Our vulnerability assessment is a preventive approach to cyber defense that regularly scans your systems for weaknesses and
Accelerate your organization’s CMMC readiness with expert guidance from 227 InfoSec. Our consultants help contractors and suppliers interpret CMMC requirements, align policies and technical controls with NIST SP 800-171, and close compliance gaps before assessment. We work side-by-side with your team to develop
227 InfoSec conducts comprehensive vessel Cybersecurity Assessments (CSA) aligned with 33 CFR Part 101, Subpart F and current USCG guidance. Assessments evaluate IT and OT systems, cybersecurity vulnerabilities, operational dependencies, critical systems, existing safeguards, and cybersecurity risks to support development and maintenance of
Partner with 227 InfoSec to expand your CMMC assessment capabilities. We have CCAs and LCAs who can be contracted to help your C3PAO organization handle overburdened schedules. We deliver trusted technical expertise, documentation validation, and evidence review to ensure clients achieve full compliance
Empower your employees to be your first line of defense! We deliver targeted security training designed to reduce human error and strengthen your first line of defense. Our team conducts custom phishing campaigns tailored to your organization, followed by targeted training.
227 InfoSec provides expert cybersecurity and compliance solutions designed to protect, strengthen, and sustain your organization’s security posture. As a Service-Disabled Veteran-Owned Small Business with decades of DoD cybersecurity experience, we deliver results-driven services that align with NIST, DFARS, and CMMC requirements. Our team works closely with clients to identify risks, enhance defenses, and build resilient security programs that support long-term operational success.

We provide end-to-end cybersecurity support, including CMMC readiness and assessor augmentation, penetration testing, and security program development. Our certified professionals help identify risks, validate controls, and implement practical security measures that keep your organization compliant and resilient.

Our team provides ongoing guidance and technical support to maintain compliance and security maturity, ensuring your environment remains protected and audit-ready.
The Cybersecurity Maturity Model Certification (CMMC) is the Department of Defense program that verifies contractors protect Federal Contract Information (FCI) and Controlled Unclassified Information (CUI). If your DoD contracts involve FCI or CUI, you will need to meet the CMMC level your contract specifies.
Level 1 covers basic safeguarding of FCI (15 requirements) with an annual self-assessment. Level 2 covers CUI using the 110 requirements of NIST SP 800-171, typically assessed by a C3PAO every three years. Level 3 adds selected NIST SP 800-172 requirements and is assessed by the government (DCMA DIBCAC).
It depends on where you are starting. Organizations with a mature NIST SP 800-171 program may only need to close gaps and organize evidence, while others need time to implement and document controls. A gap analysis or mock assessment is the fastest way to know your timeline.
A mock assessment is a practice run conducted the way a C3PAO conducts the real one. We examine your SSP and evidence, interview your team, and test configurations against each assessment objective, then deliver findings you can fix before the official assessment.
Yes. We perform vessel and facility cybersecurity assessments aligned with the U.S. Coast Guard cybersecurity final rule (33 CFR 101.650), including vulnerability identification and support for cybersecurity plans.
Answers to the questions we hear most often from defense contractors and other organizations preparing for CMMC and related compliance requirements. Don’t see your question? Contact us.
We believe cybersecurity services should be transparent, predictable, and built around measurable outcomes. Every engagement is scoped to deliver maximum value with no hidden fees, no confusing packages — just straightforward pricing aligned with your security goals.


Readiness

Lorem Ipsum is simply dummy text of the printing and typesetting industry. Lorem Ipsum has been the industry’s standard dummy text ever since the 1500s, when an unknown printer took a galley of type and scrambled it to make a type specimen book.
Lorem Ipsum is simply dummy text of the printing and typesetting industry.
227 InfoSec news and blog topics that we enjoy!
A CMMC assessor explains the most common failure we see in assessments: SSP statements that talk about a definition instead of providing one, and what assessors actually need to see.
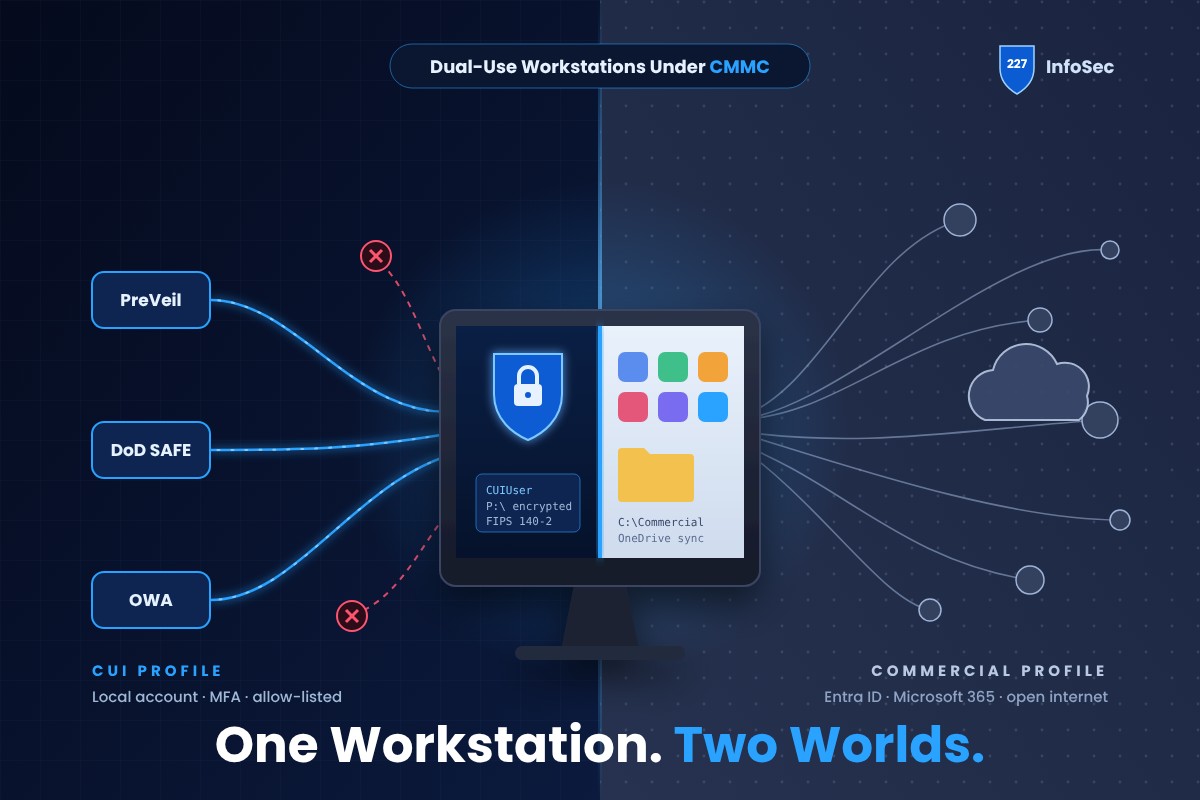
Can’t afford dedicated CUI hardware? Here’s how to configure a single workstation for both CUI and commercial work, which CMMC Level 2 practices it supports, and example SSP statements for each step.
The 227 InfoSec Monthly Newsletter covers news from 227 InfoSec and the cybersecurity industry. It comes out the first week of every month. Sign up now for free!
227 InfoSec, Inc.
Making cybersecurity obtainable for small and mid-sized businesses. CMMC consulting, assessments, and testing from a Service-Disabled Veteran-Owned Small Business.
© 2026 227 InfoSec, Inc. All rights reserved.